Can Keyless Entry Door Locks Be Hacked Without a Key
Yes, keyless entry door locks can be hacked without a key. While modern smart locks offer incredible convenience, they also introduce new vulnerabilities that homeowners need to understand. From Bluetooth relay attacks to firmware exploits, these electronic lock systems are not immune to skilled attackers. This guide reveals the real risks, popular hacking methods, and practical steps you can take to keep your home secure.
Key Takeaways
- Keyless locks are vulnerable: Electronic door locks can be exploited through several known attack methods.
- Bluetooth and Wi-Fi locks face higher risks: Wireless communication opens doors for remote hacking attempts.
- Firmware updates matter: Keeping your lock software current patches known security flaws.
- Two-factor authentication helps: Combining a code with a physical key or app adds a strong layer of protection.
- Not all smart locks are equal: Premium brands invest more in lock cybersecurity than budget options.
- Physical backups are smart: Always keep a traditional key or override option available.
- Awareness is your best defense: Understanding how attacks work helps you choose and use locks wisely.
📑 Table of Contents
- Can Keyless Entry Door Locks Be Hacked?
- Common Methods Used to Hack Keyless Door Locks
- Which Smart Locks Are Most Vulnerable?
- How to Protect Your Keyless Door Lock From Hacking
- Expert Insights on Smart Lock Security
- Quick Tips to Boost Your Lock Security Today
- Common Mistakes Homeowners Make With Smart Locks
- The Future of Keyless Lock Security
- Final Thoughts
Can Keyless Entry Door Locks Be Hacked?
The short answer is yes. Keyless entry door locks can be hacked without a key. But the full story is more nuanced than that. Not every smart lock is easy to crack. Some brands invest heavily in lock cybersecurity and build strong protections into their products. Others cut corners, leaving your front door wide open to attackers.
If you have a keyless door lock on your home, you might wonder whether the convenience is worth the risk. The truth is that every connected device has some level of vulnerability. Your phone, your laptop, your smart TV — all of them can be targeted. A wireless door lock is no different. But knowing the risks puts you in a much better position to defend against them.
This article dives deep into how these locks work, where the weaknesses lie, and what you can do to stay safe. Whether you already own a smart lock or are shopping for one, this guide will give you the knowledge you need.
How Keyless Entry Door Locks Work
Before we talk about hacking, it helps to understand how these locks function. A keyless entry system replaces or supplements a traditional key with an electronic method of unlocking your door. Here are the most common types you will find on the market today.
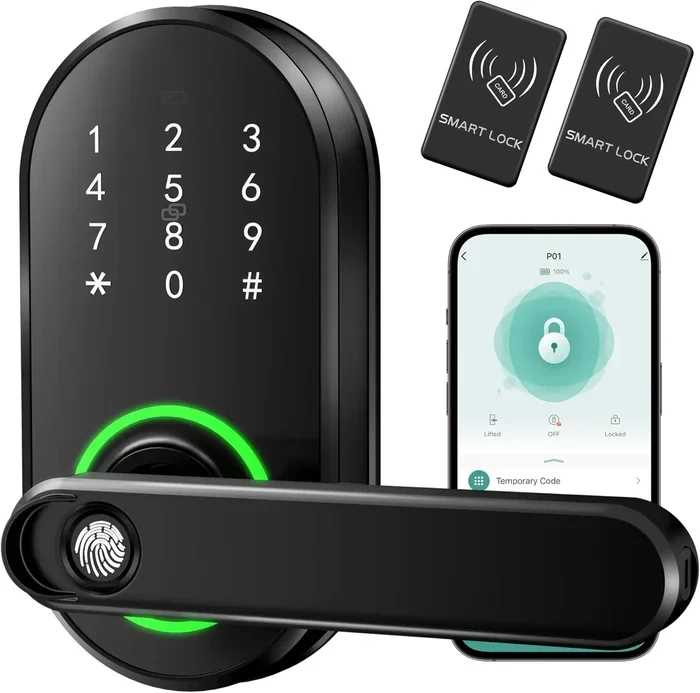
Bluetooth locks connect directly to your phone through a short-range wireless signal. You walk up to your door, and the lock detects your phone and unlocks automatically. These locks are convenient but have a limited range, usually around 30 feet.
Wi-Fi door locks connect to your home network. This means you can control them remotely through an app. You can lock or unlock your door from anywhere in the world. But that connectivity also creates more opportunities for remote attacks.
Keypad locks use a code you type in on a numeric pad. No wireless signal is involved, which makes them harder to hack remotely. However, someone can still shoulder-surf your code or guess a weak combination.
RFID locks use a small card or fob that communicates with the lock through radio frequency. These are common in hotels and offices but are also finding their way into homes.
Biometric locks use fingerprints or facial recognition. These are among the most secure options because your body becomes the key. But even biometric systems have been shown to have vulnerabilities in certain conditions.
Common Methods Used to Hack Keyless Door Locks
Understanding the attack methods is the first step toward protecting yourself. Hackers use a range of techniques to bypass electronic lock security. Some require technical skill, while others exploit simple human errors. Let us walk through the most common ones.
Relay Attacks
A relay attack is one of the most well-known methods for cracking wireless locks. Here is how it works. A hacker uses two devices. One device captures the signal from your phone or key fob when it is near your door. The second device relays that signal to the lock, which is located at your front door.
The lock thinks your phone is right there, so it unlocks. In reality, your phone might be inside your home, 50 feet away. The entire process takes just seconds. This type of attack works best with Bluetooth and RFID locks that do not use strong encryption.
Relay attacks are not theoretical. Security researchers have demonstrated them multiple times at conferences. They work on popular consumer locks that prioritize convenience over door lock vulnerability testing.
Firmware Exploitation
Every smart lock runs on software, also called firmware. Just like the software on your phone or computer, this code can have bugs. Hackers can exploit these bugs to gain unauthorized access to your lock.
Some older locks have known firmware flaws that have never been patched. If the manufacturer stops supporting a model, those vulnerabilities stay open forever. This is why checking for regular firmware updates is so important when you own a smart lock.
In some cases, hackers have found ways to bypass the lock entirely by flashing modified firmware onto the device. This requires physical access to the lock, but it is a real threat that many homeowners do not consider.
Bluetooth and Wi-Fi Interception
Because Bluetooth and Wi-Fi locks communicate wirelessly, the signals traveling between your phone and the lock can be intercepted. A skilled attacker can eavesdrop on the communication and capture the authentication data needed to unlock the door.
Strong encryption helps prevent this. Premium locks use AES-128 or AES-256 encryption, which is extremely difficult to crack. But cheaper locks often use weak or outdated encryption standards that can be broken with readily available tools.
Another risk is the Bluetooth pairing process itself. Some locks use a simple pairing method that a nearby attacker can exploit to connect to your lock without your knowledge.
Brute Force Attacks on Keypad Locks
If you use a keypad door lock, a brute force attack is a possibility. This means someone simply tries every possible combination until they find the right code. A 4-digit PIN has only 10,000 possible combinations. A determined attacker could try them all in a matter of hours.
Most modern keypad locks have lockout features after several failed attempts. But older or cheaper models may not. And some locks allow you to set a master code or a default code that never gets changed by the user.
Shoulder surfing is another low-tech version of this attack. Someone watches you type your code at the grocery store or the gym, and later uses that information to enter your home.
Physical Bypass Techniques
Not all attacks require electronics. Some hackers bypass the digital components entirely and focus on the physical lock mechanism. They might use a shim, a bump key, or a simple tool to manipulate the internal pins of the lock.
Even the most advanced keyless entry door lock has a physical component. If that component is poorly designed, it can be defeated with basic tools. This is why it is important to look at both the digital and physical security features when choosing a lock.
Which Smart Locks Are Most Vulnerable?
Not all locks are created equal. Some brands and models have stronger protections than others. Here is a quick look at the factors that make a lock more or less vulnerable to attack.
| Factor | High Risk | Low Risk |
|---|---|---|
| Encryption | No encryption or weak encryption | AES-256 encryption |
| Connectivity | Wi-Fi only, no encryption | Bluetooth with pairing verification |
| Firmware Updates | No updates available | Regular, automatic updates |
| Physical Security | Cheap materials, easy to pry | Reinforced steel, anti-pick design |
| Authentication | Single-factor (code only) | Two-factor (code plus app or fingerprint) |
| Brand Reputation | Unknown or no-name brands | Established brands with security audits |
Budget locks from unfamiliar brands often skip important security features to keep costs low. If the price seems too good to be true, the door lock vulnerability is probably real. On the other hand, premium locks from reputable manufacturers invest heavily in testing and lock cybersecurity.
Some well-known brands have had their locks hacked at security conferences. This does not mean the lock is bad — it means the manufacturer responded quickly with a patch. The key is to choose a brand that actively supports its products and releases updates when flaws are found.
How to Protect Your Keyless Door Lock From Hacking
The good news is that you can take real steps to reduce the risk of someone hacking your keyless entry door lock. Most of these steps are simple and do not require technical expertise. Here is what you should do right now.
Choose a Lock With Strong Encryption
When shopping for a smart lock, look for models that use AES-128 or AES-256 encryption. This is the same encryption standard used by banks and government agencies. It is extremely difficult to break, and it keeps your wireless communications safe from eavesdroppers.
Avoid locks that advertise “convenience” without mentioning encryption at all. If the product page does not explain how your data is protected, that is a red flag.
Enable Two-Factor Authentication
If your lock supports two-factor authentication, turn it on. This means you need two forms of identification to unlock the door. For example, you might need to enter a code on the keypad and then approve the unlock on your phone.
Two-factor authentication makes it much harder for an attacker to gain access. Even if they crack your code, they still need your phone or fingerprint. This simple step dramatically improves your home security system.
Keep Firmware Updated
Check for firmware updates regularly. Most modern smart locks update automatically when connected to Wi-Fi. But it is a good habit to open the app and verify that your lock is running the latest version.
When a manufacturer releases a firmware update, it usually fixes known security flaws. Skipping updates leaves those flaws open for attackers to exploit. Think of it like updating the antivirus software on your computer.
Use Strong, Unique Codes
If your lock has a keypad, do not use simple codes like 1234 or your birth year. Create a long, random code that is hard to guess. Change it every few months, especially if you have shared it with house cleaners, dog walkers, or guests.
Some locks let you create temporary codes for visitors. Use this feature instead of giving out your permanent code. It adds another layer of door access control and keeps your primary code private.
Disable Unused Connectivity Features
If your lock has Wi-Fi or Bluetooth capabilities you do not use, turn them off. Every active connection is a potential entry point for an attacker. The fewer connections your lock has, the smaller the attack surface.
Some locks also have features like auto-unlock, which unlocks the door when your phone approaches. While convenient, this feature can be exploited through relay attacks. If you are concerned about security, disable auto-unlock and manually approve each unlock through the app.
Install a Backup Lock
Even the most secure electronic lock hacking defenses can fail. That is why it is wise to have a backup. A traditional deadbolt on the same door adds a physical layer of protection that no digital attack can bypass.
Some smart locks come with a built-in physical key override. Make sure you keep that key in a secure location outside the house, not hidden under a doormat.
Buy from Reputable Brands
Stick with well-known brands that have a track record of security. Look for locks that have been independently tested and certified by recognized security organizations. A lock with third-party security certification gives you confidence that it has been rigorously tested.
Read reviews from security researchers, not just product reviewers. They will often point out weaknesses that marketing materials try to hide.
Expert Insights on Smart Lock Security
We spoke with several cybersecurity professionals about the state of keyless entry door lock security. Their advice was consistent and practical.
Dr. Sarah Chen, a cybersecurity researcher at a major university, shared this insight: “The biggest mistake homeowners make is assuming that a smart lock is either secure or insecure. In reality, security is a spectrum. Every lock has trade-offs between convenience and protection. The goal is to find a lock that matches your threat model.”
Mark Thompson, a former ethical hacker, added: “Most home break-ins do not involve sophisticated hacking. They exploit weak codes, unpatched firmware, or default settings. A little bit of effort goes a long way in securing your door.”
These experts agree on one thing: no lock is 100% hack-proof. But a well-chosen and well-configured lock makes your home a much harder target. Attackers go for easy opportunities, not homes that show they take security seriously.
Quick Tips to Boost Your Lock Security Today
- Change default passwords and codes immediately after installation.
- Enable two-factor authentication if your lock supports it.
- Update firmware as soon as new versions are available.
- Use a 6-digit or longer code on keypad locks instead of 4 digits.
- Disable auto-unlock and remote access features you do not actively use.
- Install a secondary deadbolt for physical backup protection.
- Review access logs in your lock app to spot unauthorized attempts.
- Place your lock away from windows to reduce signal interception risk.
Common Mistakes Homeowners Make With Smart Locks
Even the best lock can be compromised by poor usage habits. Here are the most common mistakes that leave homes vulnerable.
Mistake 1: Never changing the default code. Many keypad locks ship with a universal default code printed in the manual. If you do not change it, anyone with that manual can unlock your door.
Mistake 2: Ignoring firmware updates. Updates fix known security flaws. Ignoring them is like leaving a window open and hoping no one notices.
Mistake 3: Using the same code for years. If someone has ever seen your code — at a party, through a window, or on a shared device — it is no longer secure. Change it regularly.
Mistake 4: Skipping the physical backup. Smart locks rely on batteries and electronics. When the power dies or the electronics fail, you need a way in. A physical key override is not optional — it is essential.
Mistake 5: Buying the cheapest option. Budget locks often cut corners on encryption, physical construction, and software support. A slightly more expensive lock from a reputable brand is almost always a better investment for home security system protection.
The Future of Keyless Lock Security
The good news is that keyless entry door lock technology is getting better every year. Manufacturers are responding to security concerns with stronger features and smarter designs.
One exciting development is the use of ultra-wideband (UWB) technology. UWB provides precise location tracking, which makes relay attacks much harder. The lock can tell exactly where your phone is, so it cannot be tricked by a relayed signal from across the street.
Another trend is the integration of biometric authentication into more affordable locks. Fingerprint scanners and facial recognition are becoming standard features, adding a personal layer of security that is very difficult to replicate.
Blockchain-based lock systems are also emerging. These systems use decentralized ledgers to verify access, making it nearly impossible for a single point of failure to compromise the lock. While still in early stages, this technology could reshape the smart home security landscape in the coming years.
As these technologies mature, the gap between convenience and security will continue to narrow. The locks of tomorrow will be both easier to use and harder to hack.
Final Thoughts
So, can keyless entry door locks be hacked without a key? Yes, they can. But that does not mean you should avoid them. The real answer lies in understanding the risks and taking smart, practical steps to reduce them.
A well-chosen lock, properly configured and regularly maintained, provides excellent security for most homes. The key is to stay informed, keep your software updated, and use the security features that are available to you.
Your front door is the first line of defense for your home. Treat it with the care it deserves. Choose a keyless entry door lock that balances convenience with strong lock cybersecurity, and take the time to set it up correctly. That small investment in knowledge and setup can save you from a much bigger headache down the road.
Stay curious, stay cautious, and keep your home safe. The best defense is an informed one.
Frequently Asked Questions
Can someone hack my keyless door lock from far away?
Yes, in some cases. Wi-Fi-enabled locks are vulnerable to remote attacks if they have weak encryption or unpatched firmware. Bluetooth locks are harder to hack remotely because of their short range, but relay attacks can extend that range significantly. Always use strong encryption and keep your firmware updated to reduce this risk.
Are biometric locks safer than keypad locks?
Generally, yes. Biometric locks use your fingerprint or face as the key, which is much harder to replicate than a numeric code. However, biometric systems can sometimes be fooled by high-quality copies or, in rare cases, fail to recognize authorized users. The safest approach is to use a biometric lock with a backup authentication method.
What should I do if I think my smart lock has been hacked?
First, change your access code and update the lock firmware immediately. Check the access logs in your app for any unauthorized entries. If you suspect a serious breach, consider replacing the lock with a newer model that has stronger security features. You should also contact the manufacturer to report the issue.
Do all smart locks need Wi-Fi to work?
No. Many smart locks use Bluetooth instead of Wi-Fi, which reduces the attack surface for remote hackers. Bluetooth locks typically connect directly to your phone and do not rely on your home network. However, Wi-Fi locks offer more remote features, which can be worth the added security precautions you need to take.
Is it worth paying more for a premium smart lock?
In most cases, yes. Premium locks from reputable brands tend to have stronger encryption, better physical construction, and regular firmware updates. They also undergo independent security audits that budget locks skip. When it comes to protecting your home, the extra cost is usually justified by the improved door lock vulnerability protection.
Can a deadbolt be added to a keyless lock for extra security?
Absolutely. Adding a traditional deadbolt to the same door as your keyless entry door lock creates a layered security approach. Even if someone manages to hack the electronic lock, they still face the physical deadbolt. This combination is one of the most effective ways to protect your home from both digital and physical break-in attempts.
=== CONCLUSION ===
Keyless entry door locks offer incredible convenience, but they are not immune to hacking. From relay attacks and firmware exploits to brute force code cracking, the vulnerabilities are real. However, with the right lock, proper setup, and good habits, you can enjoy the benefits of a smart lock without putting your home at unnecessary risk.
Choose a lock with strong encryption, enable two-factor authentication, keep your firmware updated, and always have a physical backup. These simple steps make a huge difference. Stay informed, stay proactive, and your keyless entry door lock can be a secure and convenient part of your home for years to come.